About Exploitr

We're a UK-based penetration testing company

Founded in 2024 and based in South Wales, Exploitr is a CREST member company, accredited for penetration testing. We provide manual, consultant-led cyber security testing of applications, APIs and networks.

Our Story

Built to do penetration testing properly

Adam Govier spent over 12 years in penetration testing before founding Exploitr in 2024, to deliver manual, consultant-led assessments that reflect how real attackers operate, with transparent pricing and direct communication throughout.

In 2025 we launched our own platform, now the Exploitr platform, so clients can see findings as they're confirmed and track remediation between assessments.

In September 2026 Exploitr became a CREST member company, accredited for penetration testing.

Founder & Lead Consultant

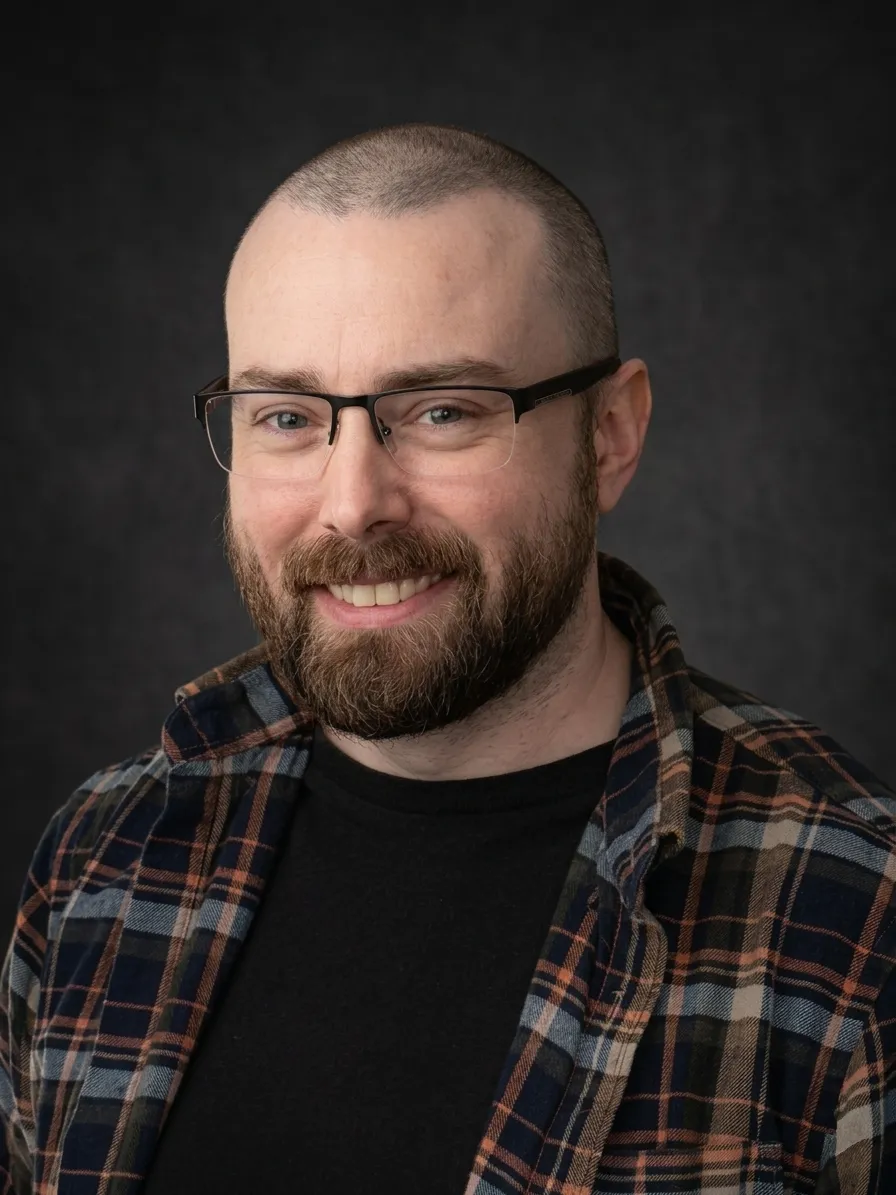
Adam Govier

Before founding Exploitr, I spent over 12 years providing penetration testing services, with a background in software development and IT administration. That experience has shaped how I approach every engagement, with the understanding that every business approaches security a little differently.

I started Exploitr because too much of what passes for penetration testing in the industry falls short. Automated scans presented as manual assessments, findings that aren't validated before being reported, and clients who finish an engagement no clearer on their actual risk than when they started. That's the standard I've set out to change.

OSCP (Offensive Security Certified Professional) OSCE (Offensive Security Certified Expert)
Adam Govier, Founder & Lead Consultant at Exploitr

Our Approach

How we think about penetration testing

These are the principles behind every engagement, whatever its size or scope.
  • We test the way attackers think

    Real attackers probe, chain findings together and look for the logic flaws scanners aren't built to find. We approach every engagement the same way, looking for the paths an attacker could take as well as the individual vulnerabilities, following our penetration testing methodology.
  • We don't do checkbox security

    Compliance frameworks like ISO 27001, Cyber Essentials Plus, and PCI DSS are valuable, but compliance is a floor, not a ceiling. Our job is to tell you what's exploitable in your environment, whether or not a framework asks us to look at it.
  • We stay in the room

    Throughout every engagement you have direct access to the consultant testing your systems, rather than a project manager or a ticketing system. When something significant is found, you hear about it immediately, not at the end of the report cycle.
  • Reports that help you fix things

    We write pentest reports that your executive and technical teams can use to understand and remediate risk, and give you access to the Exploitr platform to track and manage findings in real time.
  • We think long-term

    A single penetration test is a point-in-time snapshot, while codebases and infrastructure keep changing. That's why we offer Penetration Testing as a Service and built the Exploitr platform, so testing and visibility continue between annual assessments.
  • We hold the same standard for every client

    Whether you're a ten-person startup or a thousand-person enterprise, every engagement receives the same methodology, the same reporting standard, and the same level of care and attention. There are no second-tier clients.

Accreditations & Memberships

Our accreditations and memberships

CREST membership and Cyber Essentials are independently certified. Find out more in our Trust Centre.

CREST Member Company

As of September 2026 Exploitr is a CREST member company, accredited for penetration testing. CREST membership is assessed at the company level, examining our processes, methodologies, and quality assurance against their code of conduct and cyber security standards.

View our CREST Marketplace listing.

Cyber Essentials Certified

We hold Cyber Essentials certification, covering the baseline security controls in our own environment.

View our Cyber Essentials certificate.

UK Cyber Security Council

Exploitr has been a Corporate Member of the UK Cyber Security Council since January 2026.

Certified consultants

Our lead consultant holds the OSCP (Offensive Security Certified Professional) and OSCE (Offensive Security Certified Expert).

Our Values

The values behind our work

The work we do depends on trust. Our customers trust us to understand their security posture, give an honest assessment of their risks, and act with integrity.

These values guide how we work, how we make decisions, and how we treat people. They set the standards we hold ourselves to, even when doing the right thing is difficult. We expect them of ourselves and of one another, especially when the pressure is on.

01

Be honest, always.

Trust starts with honesty. We are open about what we find, what we know and what we don't. We don't exaggerate findings, overstate our capabilities, make promises we can't keep or hide uncomfortable truths. When we get something wrong, we say so early and put it right. Being accountable means being dependable, not infallible.

What this looks like:

  • Reporting findings accurately, without exaggeration or omission.
  • Saying what we don't know, and where our work has limits.
  • Making commitments we can keep, and telling people as soon as something changes.
  • Owning mistakes and raising them early, without blaming others.
02

Protect what we're trusted with.

Customers give us access to their systems, their data and their people, often when they are most exposed. We treat that access as a responsibility. We stay within the scope and authorisation we have agreed, protect what we see and keep it confidential.

What this looks like:

  • Testing only what we are authorised to test, and stopping to ask when we are not sure where the boundary is.
  • Handling customer data, findings and credentials securely, and deleting them as agreed.
  • Keeping what we learn about a customer confidential.
03

Use good judgement.

Technical knowledge only helps when it is applied well. We think critically, question assumptions and consider the wider context before acting. We follow our procedures, and we say so when one does not fit the situation in front of us. We value quality over speed for its own sake, and take pride in work that is thorough and useful.

What this looks like:

  • Following our procedures, and raising it when one does not fit.
  • Prioritising security outcomes that reduce real risk over ticking boxes.
  • Taking the time to understand a problem and explaining the answer in plain language.
04

Speak openly.

Good decisions depend on honest conversations. We challenge ideas and raise concerns respectfully, whatever our seniority. We admit when we are wrong, ask for help and say when we don't know. Disagreement is part of getting to the right answer.

What this looks like:

  • Challenging assumptions and decisions when we have concerns.
  • Listening to different perspectives without getting defensive.
  • Creating an environment where people can speak up without fear of humiliation or retaliation.
05

Do right by the customer.

We take our customers' goals seriously and treat them fairly. We are upfront about pricing, honest about what we can deliver and focused on work that addresses their needs. We give customers the benefit of our expertise, even when it is not what they hoped to hear, so they can make informed decisions.

What this looks like:

  • Setting expectations early and avoiding false promises or unnecessary complexity.
  • Challenging a request when it will not achieve the intended outcome.
  • Recommending what is right for the customer, not simply what is easiest to sell.
06

Get better, together.

We are ambitious about the quality of our work and the people we become. We take ownership of our development, keep improving our skills and judgement, and look for ways to do things better. We want to do well as individuals and as a team, so we share what we learn and help one another improve.

What this looks like:

  • Seeking feedback and acting on it.
  • Taking initiative and continually developing our expertise.
  • Sharing knowledge, supporting colleagues and helping the whole team succeed.

In the press

Expert commentary and features

01

TechRound

Adam was quoted in TechRound's coverage of the Booking.com data breach, explaining how attackers use leaked booking details to make phishing attempts convincing. Read the article.
02

ConsumerAffairs

Adam contributed expert commentary on what to do after a data breach, covering the steps individuals should take to protect their identity in the aftermath of an incident. Read the article.
03

Spiceworks

Adam provided insights on the role of a penetration tester, and what skills and qualities businesses look for in individuals when hiring for this role. Read the article.

Scope your next assessment with Exploitr

Our team are on hand to discuss your requirements and scope a penetration test or cyber security assessment that meets your needs. A 30-minute scoping call is all it takes to get started.

If you're a consultant, MSP, or trusted adviser with clients who need security testing, see our referral partner programme.