Adam Govier
Founder & Lead Consultant
Adam founded Exploitr and leads its penetration testing practice. He holds OSCP and OSCE certifications and has over 12 years' experience in penetration testing and security consulting, with a background in software development and IT administration.
Accreditations and memberships


Security Alerts
Node2Shell (HTTP2Shell) Brotli Remote Code Execution (CVE-2026-111497)
Security Alerts
PHP2Shell Remote Code Execution (CVE-2026-109618, CVE-2026-109619)
Penetration Testing
How often should you get a penetration test?
Company News
Exploitr is Now a CREST Member Company, Accredited for Penetration Testing
Web Application Security
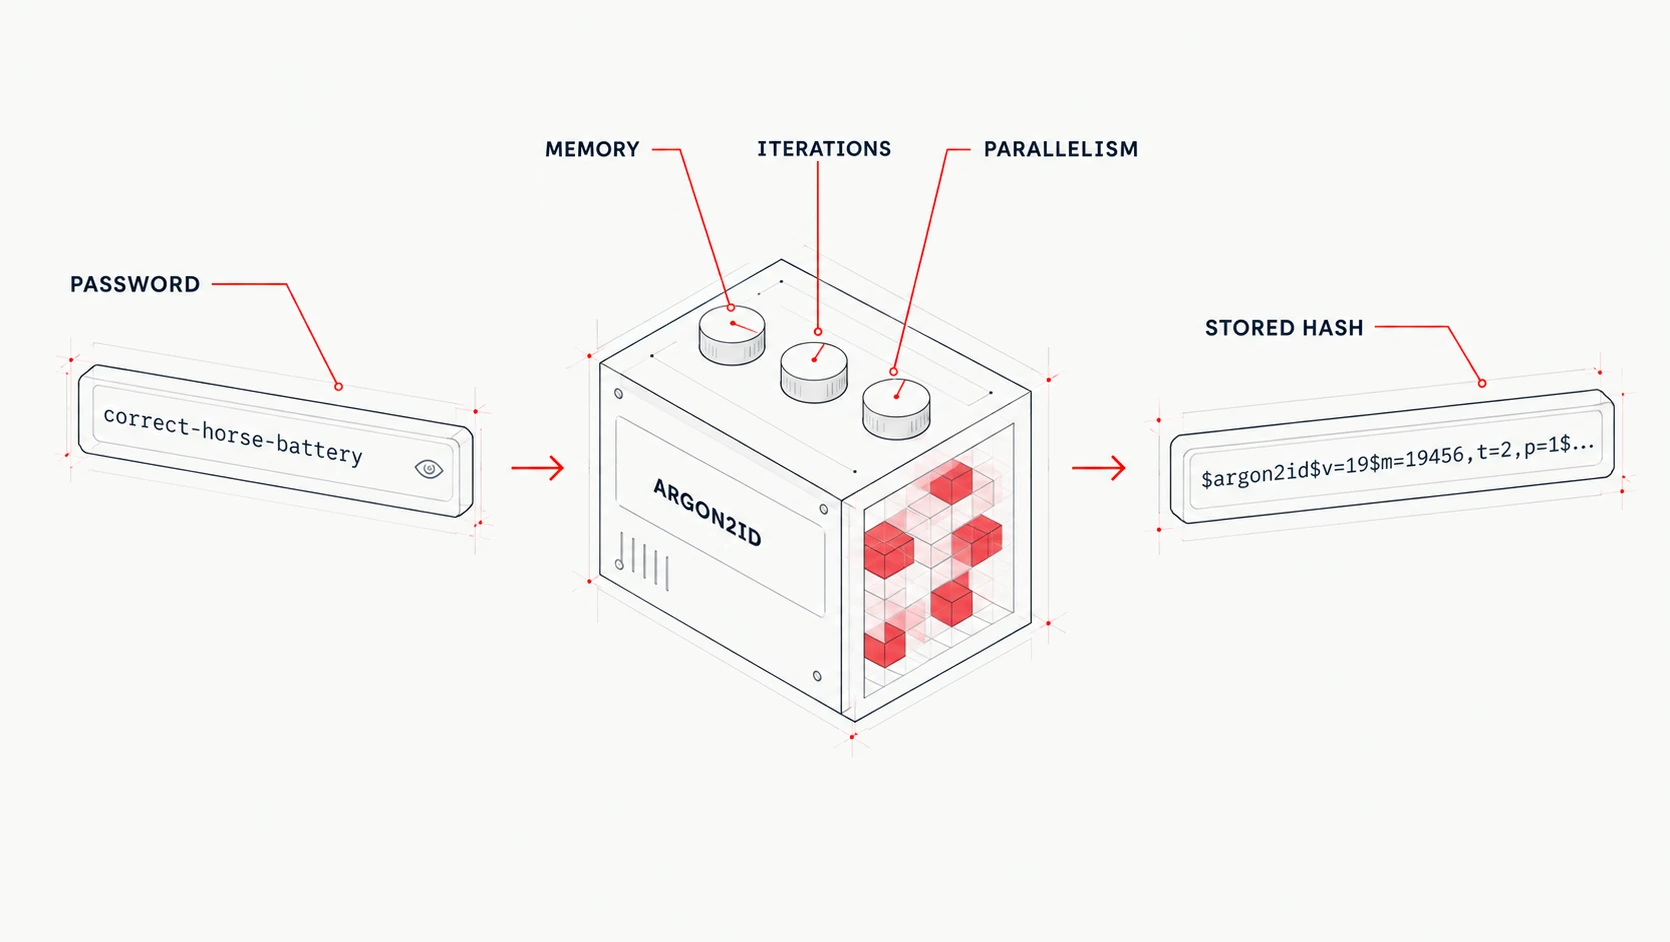
Password storage: Argon2id, bcrypt, and scrypt compared
Penetration Testing
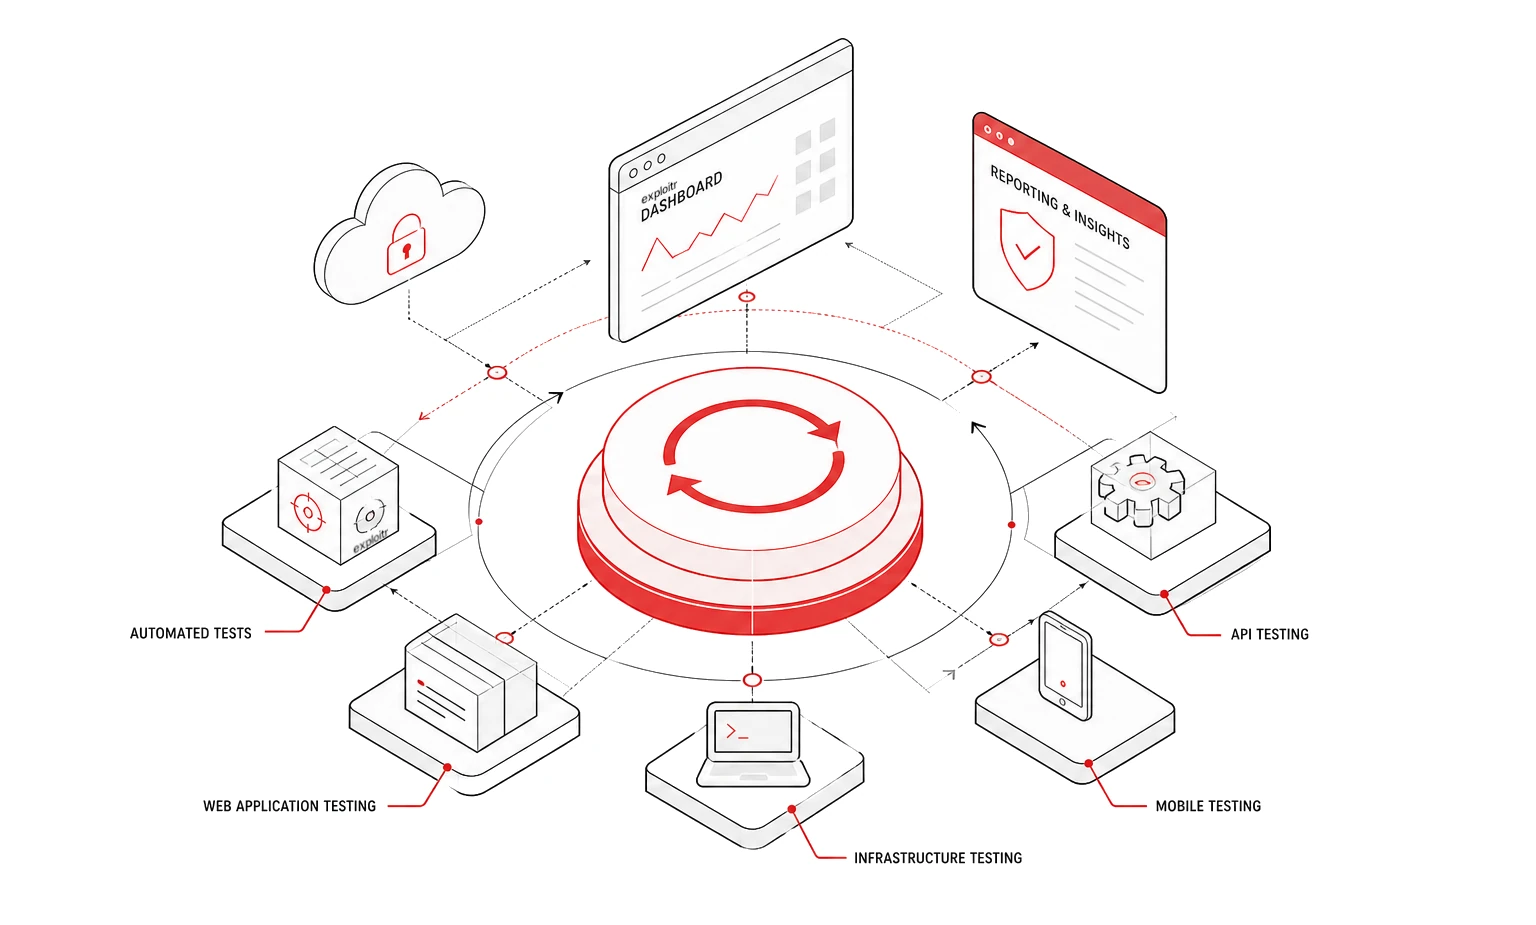
Why a once-a-year penetration test is not enough
Penetration Testing
How to choose a penetration testing provider in the UK
Vulnerability Management
Vulnerability scanning vs penetration testing: which one do you need?
Penetration Testing
Manual vs automated penetration testing: How to tell what you're paying for
Network Security
What is network penetration testing?
Penetration Testing
Assumed Breach Penetration Testing Explained
Supply Chain Security
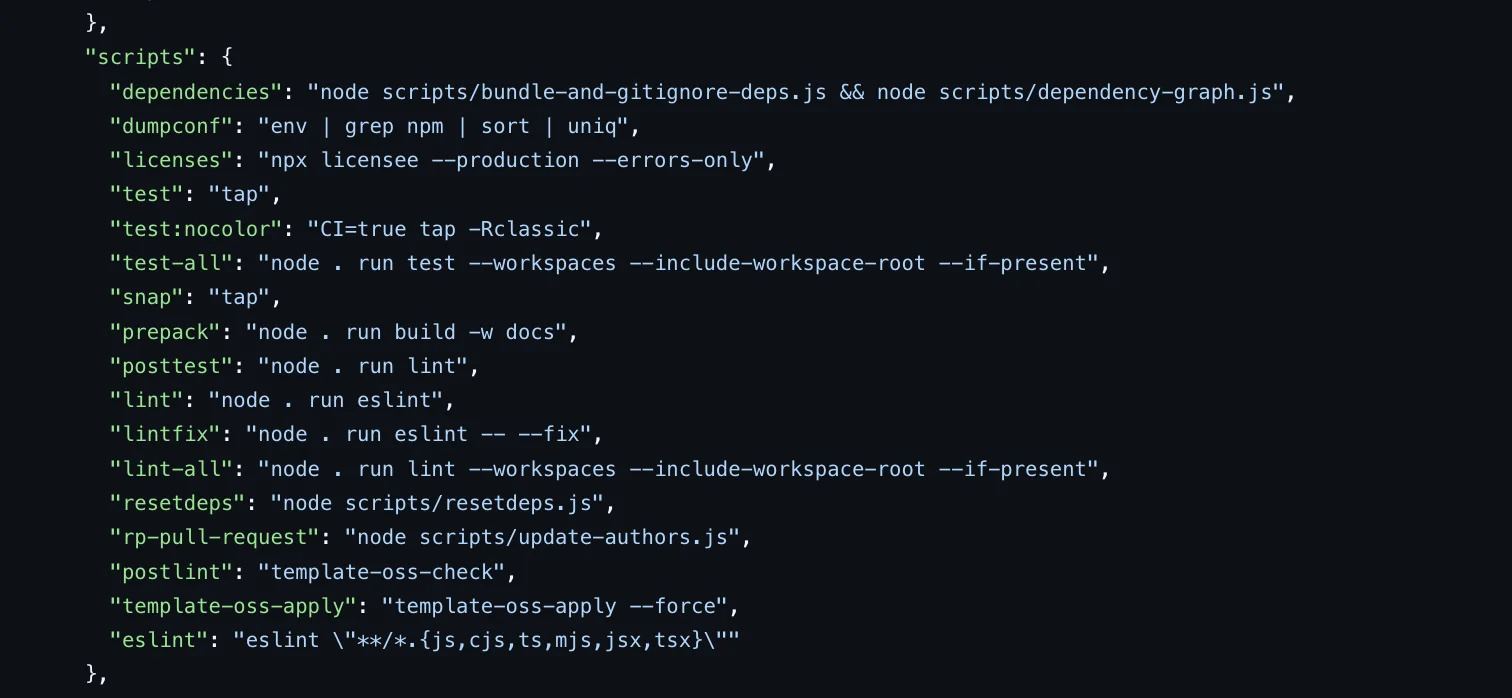
npm v12: Mitigating Supply Chain Attacks with New Install Controls
Penetration Testing
How to Write a Penetration Test Report
Web Application Security
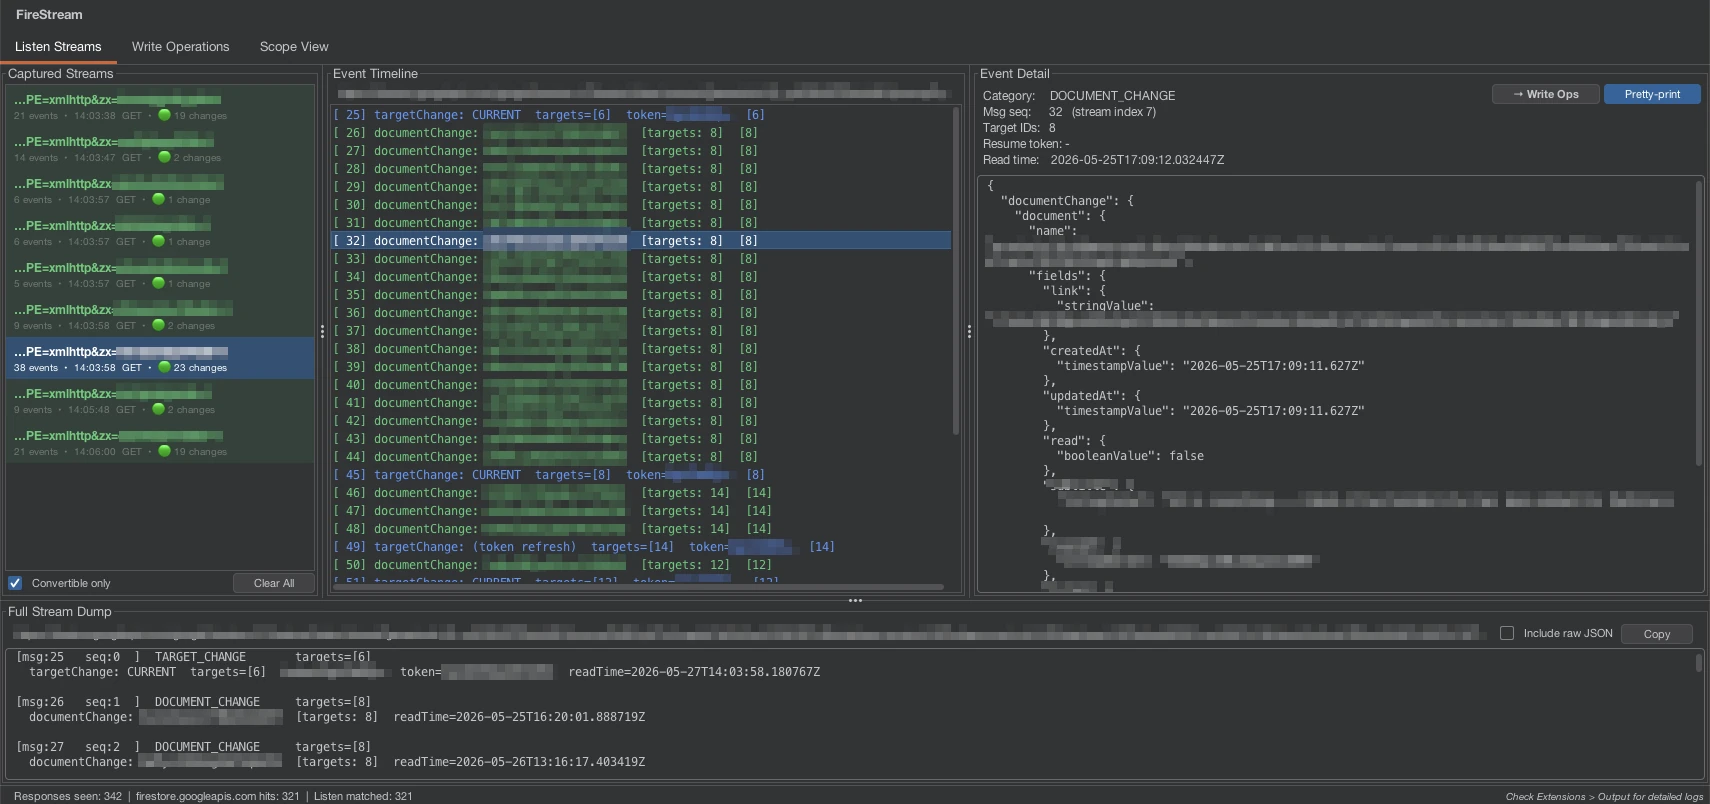
Intercepting and Manipulating Firestore Streams with a Custom Burp Extension
Security Alerts
Alert: GitHub Investigates Internal Repository Breach via Malicious VS Code Extension
Security Alerts
Alert: Copy Fail Linux Local Privilege Escalation (CVE-2026-31431)
Security Alerts
Alert: GitHub Bug Exposed Webhook Secrets to Recipient Endpoints
Web Application Security
What to Expect During a Web Application Pentest
Supply Chain Security
Dependency Pinning for npm: Defending Against Supply Chain Attacks
Email Security
Secure your email with MTA-STS
Web Application Security
Authentication Security for SaaS Startups: What to Get Right
AI Security
Is Your Penetration Test Leaking Data to Third-Party AI?
Network Security
Mitigating LLMNR Poisoning Attacks
Network Security
Scoping a network penetration test
Web Application Security
Scoping a web application penetration test
Network Security
OK, now it's really time to disable Net-NTLMv1
AI Security
When Security Issues Kill the Vibe (Coding)
Email Security
What is DKIM? How DomainKeys Identified Mail Works & How to Set It Up
Email Security
DMARC: how it works, setup and policy guide
Email Security
What is SPF? Sender Policy Framework Explained & How to Configure It
Web Application Security
What is XSS? Cross-Site Scripting Explained
Web Application Security
What is SQL Injection (SQLi)?
Exploit Development
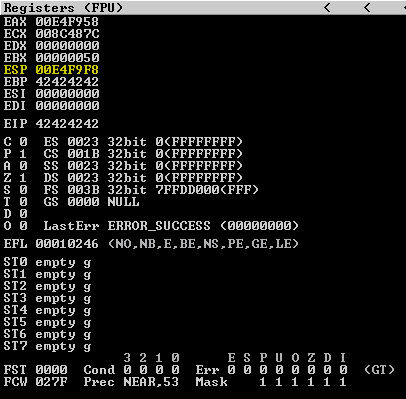
Identifying Bad Characters in Exploit Development
Email Security
Email Phishing Attacks Explained
Network Security
What is Password Cracking and How Does it Work?
Company News
Exploitr Gains CREST Pathway Status
Penetration Testing
What is a Red Team Engagement?
Penetration Testing
What is penetration testing?
Vulnerability Management
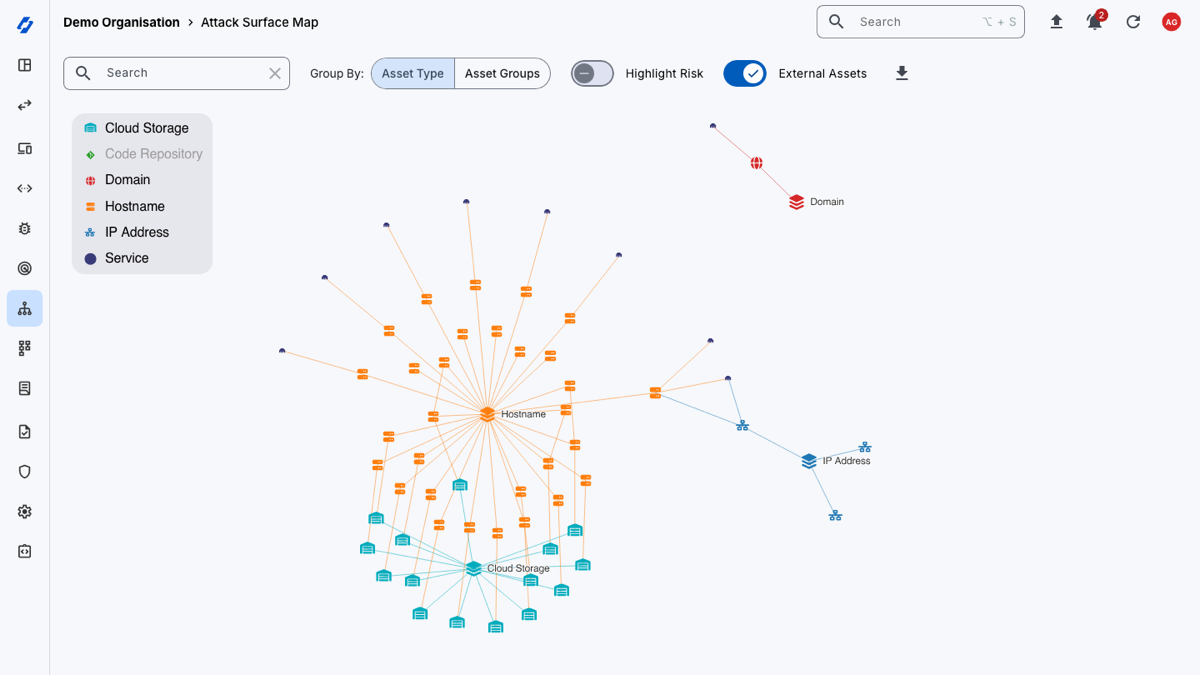
What is External Attack Surface Management (EASM)?
Vulnerability Management
Common Vulnerability Management Challenges
Exploit Development
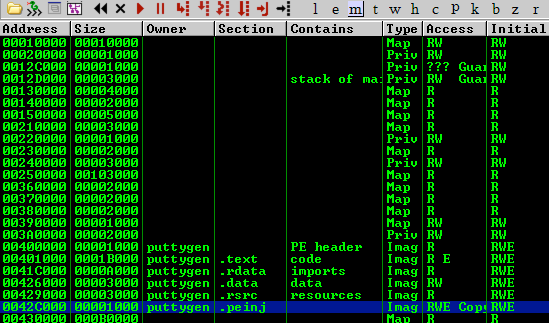
Manually Implanting Backdoors in PE Files
Exploit Development
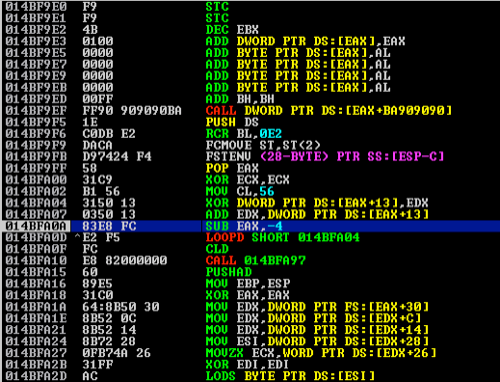
Using an Egghunter to Exploit Minimal Buffer Overflows
Company News
Cyber Essentials Certified
Exploit Development
An Introduction to Exploiting Basic Vanilla Buffer Overflows

Network Security
Understanding WPA/WPA2 Pre-Shared-Key Cracking
Get a fixed-price quote for your penetration test
Our team will help you scope the right assessment for your environment and agree a fixed price before testing starts.