Continuous Penetration Testing (PTaaS)
Penetration Testing as a Service
Extend your security team with Exploitr's continuous security testing. Predictable fixed costs, scalable to your needs, with expert consultant-led testing throughout.
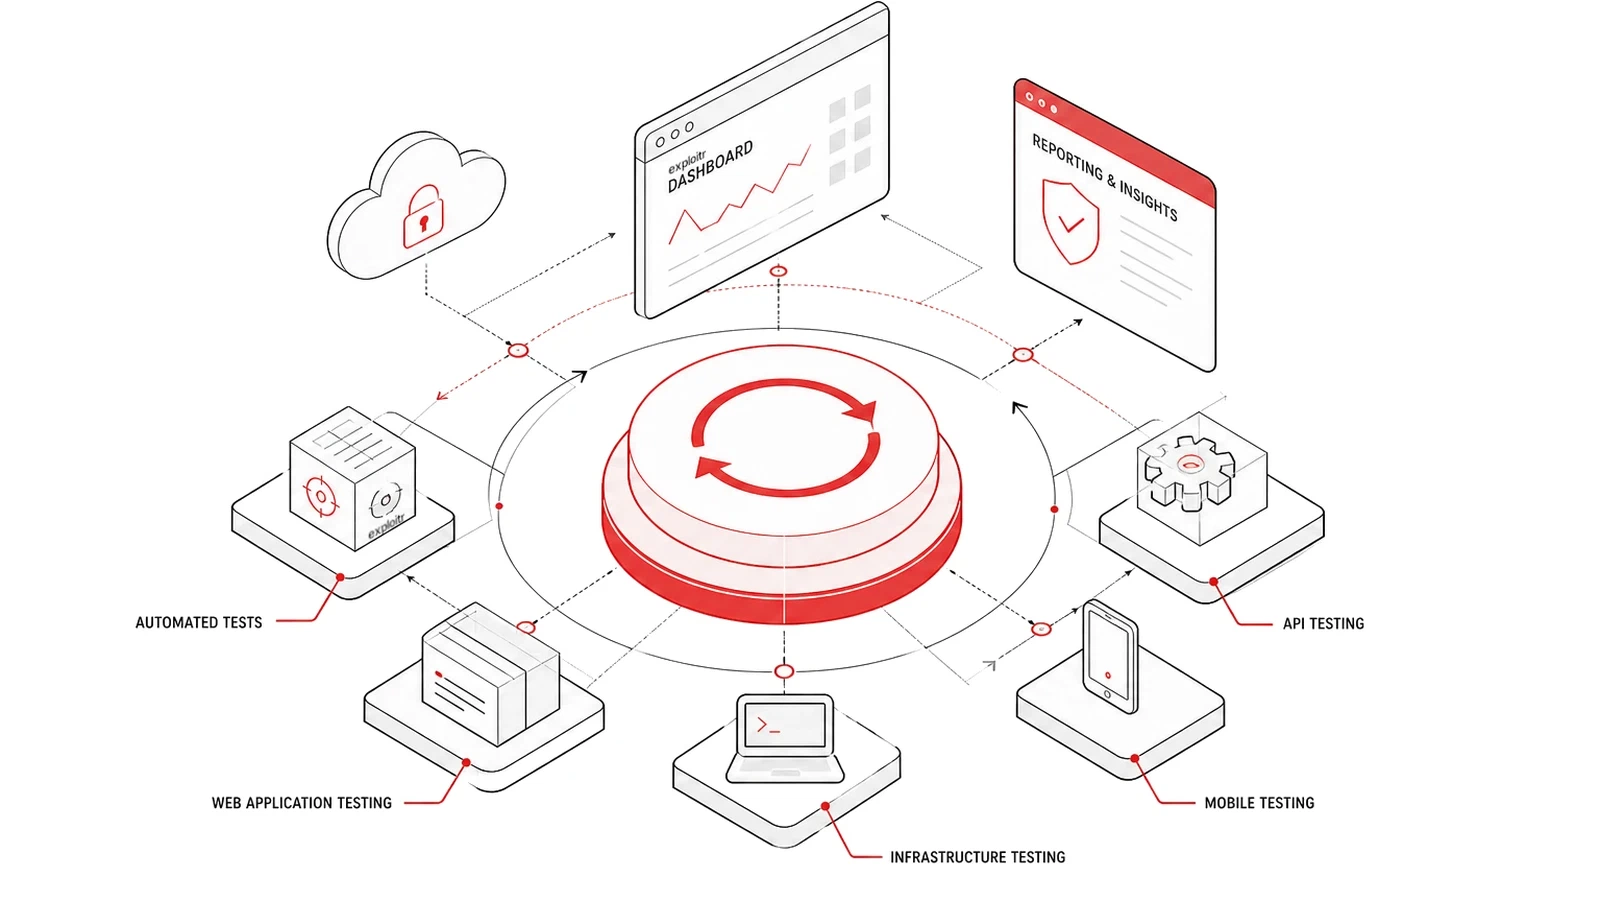
Penetration Testing as a Service


What is PTaaS?
Penetration Testing as a Service (PTaaS), sometimes called continuous security testing, delivers ongoing manual penetration testing through a fixed monthly retainer. Your attack surface is assessed as your product, infrastructure and team change, rather than once a year.
An organisation shipping features weekly can introduce new endpoints, infrastructure changes and regressions between annual tests that no one has looked at. With PTaaS, testing keeps pace with those changes, and you have a continuous record of testing for compliance.
Engagements start from £5,700 per month and are delivered by UK-based consultants working directly with you throughout.
Included every month
Why penetration test as a service?
Is PTaaS Right for You?
How PTaaS Works
We work with you to define assets, environments, and rules of engagement upfront. You approve the scope and we operate within it for the duration of the subscription, so there are no repeat scoping calls or new contracts each time testing starts.
If your environment changes significantly, scope can be adjusted by agreement.
Direct and schedule testing yourself, or allow our consultants to independently pursue the highest-risk attack paths within your approved scope.
We can align with your sprint or release cadence, test ahead of key deployments, or run on a continuous rolling basis between changes. The approach is agreed at the start and can be adjusted as your delivery rhythm evolves.
Findings are delivered as testing happens via the Exploitr platform, not weeks later in a static PDF.
You see vulnerabilities as they are discovered, with severity ratings, reproduction steps, and remediation guidance available immediately. Your development team can begin remediation while testing is still in progress.
Use our platform to track the status of every finding from discovery through to remediation. Fix an issue and request a retest directly within the platform, without starting a new engagement or re-scoping the work.
Retesting is included within your monthly subscription, so there are no additional charges to verify that a vulnerability has been resolved.
From £5,700/mo
for continuous penetration testing
Not sure what level of coverage your organisation needs? A 30-minute scoping call is free and gets you a fixed written quote.
No obligation · Strictly confidential · Reply within one business day
| PTaaS Standard: 5 testing days/month | From £5,700/mo |
| PTaaS Advanced: 10 testing days/month | From £11,100/mo |
| PTaaS Scale: 15 testing days/month | From £16,200/mo |
| PTaaS Dedicated: 20 testing days/month | From £21,000/mo |
All plans are fixed-price and all-inclusive. The difference between tiers is capacity, not tester seniority or testing depth.
Larger subscriptions benefit from preferential pricing because we can allocate consistent tester availability and reduce scheduling overhead. All plans have a minimum 6-month term, and a 12-month term attracts a further discount, confirmed in your written quote.
Compare all our penetration testing services.
Common Questions
A testing day represents up to 8 hours of active manual penetration testing and reporting performed by an experienced tester.
Testing time includes:
manual testing and exploitation
analysis and validation of findings
writing findings and remediation guidance
and coordination with the customer.
It does not include sales or account management overhead.
PTaaS starts from £5,700 per month for 5 testing days, or from £11,100 per month for 10 testing days. Pricing is based on the volume of testing time you contract each month, so it scales with how much of your environment needs regular testing.
Plans run on a minimum 6-month term. If you commit to 12 months, we apply a further discount, which we confirm in your written quote.
Our penetration testing pricing guide compares costs across every service.
Yes. All plans are all-inclusive. There are no additional charges for reporting, retesting, or reasonable clarification sessions.
PTaaS can be used to cover most of our testing services, including web application pentesting, external penetration testing, internal network penetration testing, and API pentesting.
Unused days expire at the end of each month. Capacity is reserved exclusively for you, ensuring availability when you need it.
Yes. Scope can be adjusted by agreement and you can upgrade your plan at any time. We require written authorisation for testing but will make this as easy as possible as part of our ongoing service.
We work best when considered an extension of your team.
A common pattern is a pre-engagement meeting before a staging or production release, then testing begins when the environment is ready. We adapt to your sprint cadence, not the other way around.
A standard penetration test is a one-off engagement with a fixed scope and a single report. PTaaS replaces that with a monthly retainer providing:
ongoing testing capacity
continuous finding visibility through our platform
a consultant who builds familiarity with your environment over time.
The cost is predictable, coverage is continuous, and retesting is included.
PTaaS produces a continuous record of security testing activity throughout the year: dated test records, findings with severity ratings and remediation guidance, and retest confirmations as issues are resolved.
Neither ISO 27001 nor SOC 2 mandates penetration testing by name, but auditors commonly ask for testing evidence, and a twelve-month PTaaS testing log is straightforward to present to an auditor or assessor.
We can provide findings exports and reporting in formats suited to your audit requirements on request.